

Business Email Compromise by the Numbers: What the Latest Stats Reveal
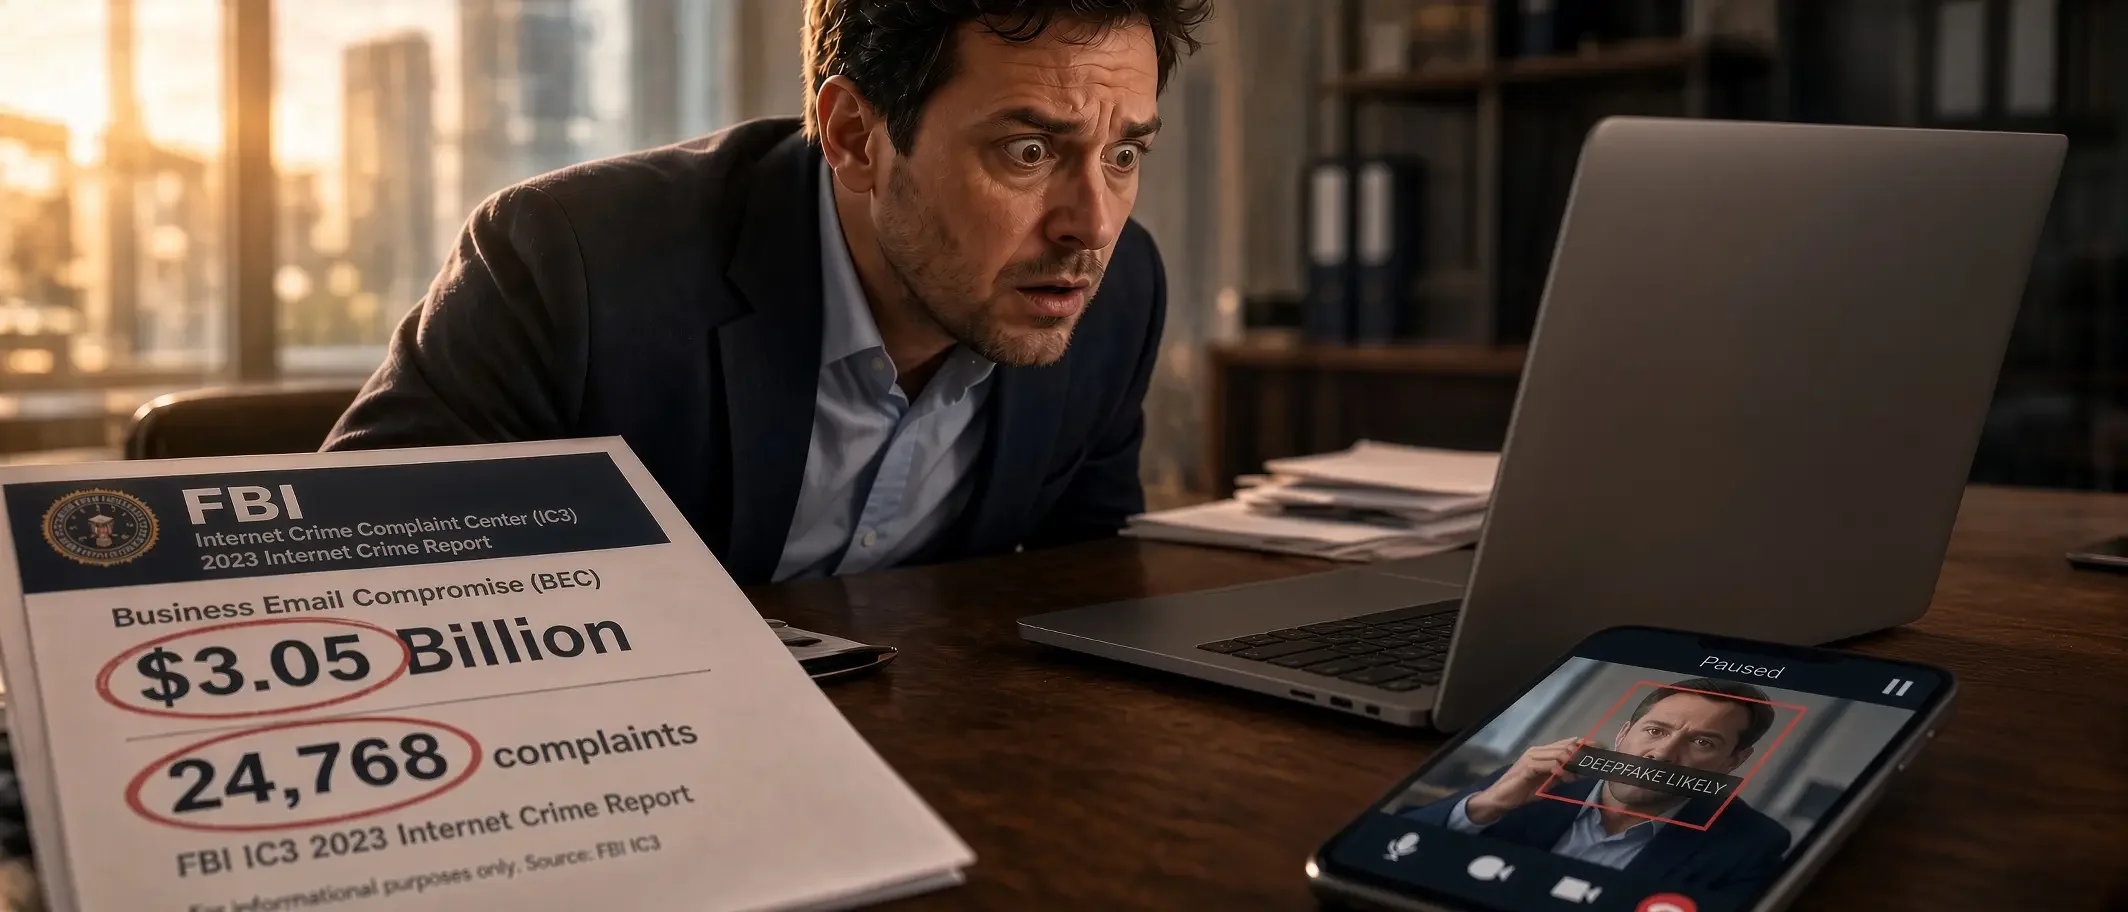
Business Email Compromise doesn’t make the same headlines as ransomware. There’s no locked screen or dramatic ransom note. The money simply leaves the account, often after what looked like a routine email.
The numbers show just how effective this quiet approach remains.
The Scale of the Problem
According to the FBI’s Internet Crime Complaint Center (IC3) 2025 report, Business Email Compromise generated $3.046 billion in reported losses across 24,768 complaints. That works out to an average of roughly $123,000 per incident.
BEC ranked as the second-highest loss category overall, trailing only investment fraud. Total cybercrime losses reported to the IC3 reached $20.877 billion in 2025—a 26% jump from the previous year.
These figures only reflect cases that were reported. Many smaller incidents never make it into official statistics.
What the Numbers Tell Us About How Attacks Work
Several patterns stand out from recent data:
A large share of BEC activity still targets payment processes—invoice redirection, vendor bank detail changes, and urgent wire requests.
Microsoft 365 environments continue to dominate as the primary attack surface.
Multi-factor authentication is frequently bypassed. In one mid-market study of BEC incidents, MFA was circumvented in roughly 79% of cases, often through session hijacking techniques.
Vendor impersonation has grown more common than pure internal “CEO fraud” in many datasets.
AI is showing up more often. The IC3 specifically noted over $30 million in BEC losses tied to AI-assisted scams in 2025, including improved writing and voice cloning used in follow-up calls.
The average loss per complaint sits in the low six figures, but individual cases can climb much higher when a successful attack hits a larger payment or a series of transactions.
Why Small and Mid-Sized Businesses Feel It
SMBs make up the bulk of reported BEC victims in multiple analyses. They often lack the layered approval processes and dedicated fraud teams that larger organizations maintain. A single person handling accounts payable or vendor management can become the entire control point.
Healthcare practices, professional service firms, retailers, and government contractors all process regular payments and maintain ongoing vendor relationships—exactly the conditions attackers look for.
What the Data Suggests About Defense
The statistics point to a few practical realities:
Financial process controls matter as much as technology. Out-of-band verification for payment changes and wire requests continues to stop attacks that technical filters miss.
MFA remains necessary but is no longer sufficient on its own. Monitoring for unusual mailbox rules, session anomalies, and forward configurations adds meaningful protection.
Speed of detection makes a measurable difference. In environments with active monitoring, dwell times for BEC activity can drop from days to minutes.
The Bottom Line
Business Email Compromise remains one of the most financially damaging cyber threats facing organizations of all sizes. The 2025 numbers—over $3 billion in reported losses and tens of thousands of complaints—show that the problem is not fading.
The attacks succeed because they look ordinary and arrive at moments when people are under pressure to act. Organizations that treat payment requests with consistent verification, regardless of how familiar the sender appears, are the ones most likely to keep those losses off their own books.
If your current process for approving payments or updating vendor details still relies primarily on email, the latest statistics suggest it’s worth a second look.